Certification preparation
Certified Information Security Manager (CISM)
Five-day course where learners practise information security governance, risk, programme delivery and incident response, with labs and exam prep.
THE BIG PICTURE
About this course
Certified Information Security Manager (CISM) is a globally recognised certification for information security managers awarded by ISACA. It validates the ability to govern, manage risk, run an information security programme, and handle incidents aligned to business objectives. Across five days, the course follows the four CISM domains with practical work: building governance charters, mapping risks, designing programme roadmaps, and planning incident response. Learners use templates and case studies, perform hands-on analysis, and complete daily exam-style question sets. The CISM exam has 150 multiple-choice questions in 240 minutes, closed book, delivered online via remote proctoring or at test centres. ISACA uses a scaled score, requiring 450/800 to pass. After passing, candidates have five years to apply for certification with experience; certification is maintained through CPE (120 hours over three years, minimum 20 annually) and an annual maintenance fee. ISACA owns the certification scheme. MindClick provides training and exam preparation and is not an accredited or authorised partner.
What you’ll learn
- Explain the purpose and components of an information security governance framework
- Apply risk identification, analysis and treatment methods to produce a defensible risk register
- Design an information security programme operating model with roles, budgets and metrics
- Integrate security requirements into projects, third-party management and change processes
- Plan and coordinate incident response, investigation, communication and recovery activities
- Develop governance and reporting artefacts for senior management and audit stakeholders
- Evaluate control effectiveness and define continuous improvement actions using programme metrics
- Practise CISM-style questions and create a personal study plan to prepare for the exam
A CLEAR PATH FORWARD
5-day course agenda
5 instructor-led days (40 contact hours) mapped to the exam domains. Each day combines short concept sessions, hands-on practice on a running case study and exam-style questions.
- Learning route
- 5 recommended days
- Practical work
- 5 guided activities
- Finish with
- Mock exam + certification exam
Take a look at each day. Open a section to see the topics and practical work.
Day 1Information Security Governance EssentialsDomain 1 – Information Security Governance
What we’ll cover
- 09:00–10:30 · Course overview, CISM exam orientation, and the role of the security manager
- 10:45–12:30 · Governance frameworks and alignment with enterprise objectives (e.g., COBIT, ISO/IEC 27001)
- 13:30–14:30 · Policies, standards, procedures and guidelines: hierarchy and ownership
- 14:30–15:15 · Governance metrics, reporting lines and engagement with senior stakeholders
- 15:30–16:15 · Building an information security strategy and governance charter
- 16:15–17:00 · Exam-style practice questions: Information Security Governance
- 17:00–17:30 · Daily debrief and learning log
Put it into practice
Create an information security governance charter for a sample organisation, mapping objectives to business goals. Peer review the charter and refine accountability and reporting lines.
You’ll take away
Completed governance charter template
Day 2Information Security Risk ManagementDomain 2 – Information Security Risk Management
What we’ll cover
- 09:00–09:30 · Recap of Day 1 and warm-up quiz
- 09:30–10:30 · Risk management concepts, context setting and risk criteria
- 10:45–12:30 · Risk identification techniques, asset valuation and stakeholder input
- 13:30–14:30 · Threats, vulnerabilities, likelihood and impact analysis
- 14:30–15:15 · Qualitative and quantitative analysis, risk aggregation and validation
- 15:30–16:15 · Risk treatment options, control ownership and risk acceptance
- 16:15–17:00 · Exam-style practice questions: Risk Management
- 17:00–17:30 · Daily debrief and Q&A
Put it into practice
Build a risk register for a given case study, including risk statements, causes, impacts and owners. Propose and justify treatment plans aligned to defined risk criteria.
You’ll take away
Risk register and treatment plan
Day 3Information Security Program DesignDomain 3 – Information Security Program
What we’ll cover
- 09:00–09:30 · Recap of Day 2 and quick knowledge check
- 09:30–10:30 · Programme charter, scope, operating model and governance interfaces
- 10:45–12:30 · Control selection and design aligned to risk; policy lifecycle management
- 13:30–14:30 · Resource planning, budgeting and sourcing (internal, managed, cloud)
- 14:30–15:15 · Metrics and KPIs/KRIs for programme performance and assurance
- 15:30–16:15 · Security awareness, training and culture change planning
- 16:15–17:00 · Exam-style practice questions: Information Security Program
- 17:00–17:30 · Daily debrief and action points
Put it into practice
Draft a one-year information security programme roadmap with milestones, budget assumptions and metrics. Present the roadmap and receive feedback focused on feasibility and alignment.
You’ll take away
Programme roadmap and metrics pack
Day 4Programme Operations and Incident ManagementDomain 3 – Programme operations; Domain 4 – Incident Management foundations
What we’ll cover
- 09:00–09:30 · Recap of Day 3 and discussion of key takeaways
- 09:30–10:30 · Operational oversight, change management and third‑party security
- 10:45–12:30 · Continuous monitoring, logging and vulnerability management
- 13:30–14:30 · Incident response lifecycle, roles and communication
- 14:30–15:15 · Coordinating with legal, privacy, HR and external parties
- 15:30–16:15 · Tabletop walk‑through of an incident scenario and decision points
- 16:15–17:00 · Exam-style practice questions: Program and Incident domains
- 17:00–17:30 · Daily debrief and lessons learned
Put it into practice
Run a facilitated tabletop exercise for a ransomware incident, capturing actions, decisions and communication paths. Compile immediate improvements for detection, response and recovery.
You’ll take away
Incident response playbook draft
Day 5Advanced Incident Management and Exam ReadinessDomain 4 – Incident Management; full-domain review and exam strategy
What we’ll cover
- 09:00–09:30 · Recap of Day 4 and readiness checkpoint
- 09:30–10:30 · Forensics considerations, evidence handling and chain of custody (manager’s view)
- 10:45–12:30 · Business continuity, disaster recovery alignment and post‑incident improvement
- 13:30–15:15 · Timed mock exam (mixed domains, CISM-style questions)
- 15:30–16:15 · Mock exam review, rationale and targeted remediation
- 16:15–17:00 · Exam booking guidance and certification application steps
- 17:00–17:30 · Course wrap‑up, personal study plan and next steps
Put it into practice
Sit a timed mock exam under exam-like conditions, followed by a facilitated review to analyse reasoning and common traps. Finalise a personal study and booking plan.
You’ll take away
Personal exam study plan and booking checklist
Bring it all together
Certification exam: ISACA Certified Information Security Manager (CISM) Exam, awarded by ISACA. 150 multiple-choice questions, 240 minutes, Closed book, Online remote proctored or test centre. Pass mark: Scaled score of 450/800. Validity: Certification maintenance requires 120 CPE hours over 3 years (minimum 20 annually) and an annual maintenance fee; exam pass is valid for 5 years toward certification application.. Every attendee also receives a MindClick certificate of completion for 40 contact hours.
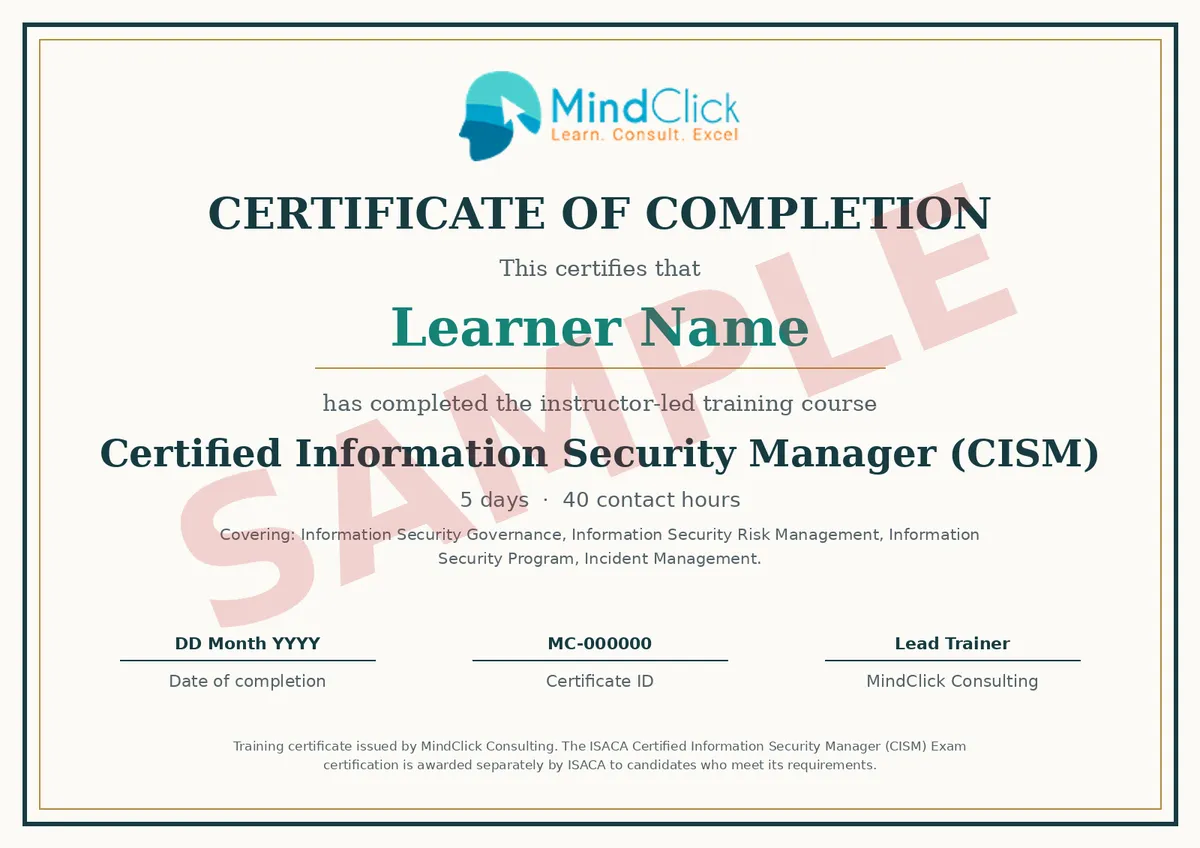
What you receive
You earn two separate credentials. The sample shows the MindClick training certificate.
- MindClick certificate of completion: 5 days, 40 contact hours, issued to every attendee who completes the course.
- ISACA Certified Information Security Manager (CISM) Exam: issued by ISACA when you meet its requirements and pass the exam.
Before you choose your learning route
Certification route: Certification award also requires verified professional experience and a successful application to ISACA.
Session timings are indicative; the trainer may adjust them for the group. Exam details reflect the awarding body’s published information at the time of writing; confirm the current version when you book.
ISACA owns this certification scheme. MindClick provides training and exam preparation and is not an accredited or authorised partner of ISACA.
Fees
| Delivery format | Fee per learner | Exam fee |
|---|---|---|
| Live online | $2,800 USD | Included |
| Classroom | $4,500 USD | Included |
One awarding-body certification exam attempt is included in the training fee. Confirm the current fee, any applicable tax and what the fee covers in writing before you pay.
Prerequisites
- There is no formal prerequisite to sit the CISM exam; certification requires at least five years of information security management experience (with allowable substitutions per ISACA policy). Recommended: prior experience in information security or IT governance; bring a laptop with Wi‑Fi and a spreadsheet tool for classroom exercises.
FIND YOUR START
Confirmed batch starts
Choose a published start, then review your offer in the same enrollment flow. A start date is not the full timetable or a seat reservation.
Choose your country & monthStarts
- Training location
- Manama, Bahrain
- Local timezone
- Asia/Bahrain
Venue and full session timetable to be supplied.
Starts
- Training location
- Cairo, Egypt
- Local timezone
- Africa/Cairo
Venue and full session timetable to be supplied.
Starts
- Training location
- Kuwait City, Kuwait
- Local timezone
- Asia/Kuwait
Venue and full session timetable to be supplied.
Starts
- Training location
- Muscat, Oman
- Local timezone
- Asia/Muscat
Venue and full session timetable to be supplied.
Starts
- Training location
- Doha, Qatar
- Local timezone
- Asia/Qatar
Venue and full session timetable to be supplied.
Starts
- Training location
- Riyadh, Saudi Arabia
- Local timezone
- Asia/Riyadh
Venue and full session timetable to be supplied.
Frequently asked questions
How long is the course?
5 days, 40 contact hours, normally 09:00 to 17:30 with breaks. The agenda follows the exam domains and the final day includes a mock exam.
What is the exam format?
ISACA Certified Information Security Manager (CISM) Exam: 150 multiple-choice questions, 240 minutes, Closed book, Online remote proctored or test centre. Pass mark: Scaled score of 450/800. Confirm the current version with the awarding body when you book.
Is the exam included?
Yes. Outside India the fee includes one certification exam attempt. Retakes are booked and paid directly with the awarding body. Certification award also requires verified professional experience and a successful application to ISACA.
Are there prerequisites?
There is no formal prerequisite to sit the CISM exam; certification requires at least five years of information security management experience (with allowable substitutions per ISACA policy). Recommended: prior experience in information security or IT governance; bring a laptop with Wi‑Fi and a spreadsheet tool for classroom exercises.
What certificate will I receive?
Two credentials. MindClick issues a certificate of completion for 40 contact hours to every attendee. ISACA issues the ISACA Certified Information Security Manager (CISM) Exam certification when you pass the exam and meet its requirements. Certification maintenance requires 120 CPE hours over 3 years (minimum 20 annually) and an annual maintenance fee; exam pass is valid for 5 years toward certification application..
Is MindClick an accredited training partner for this certification?
MindClick provides training and exam preparation and is not an accredited/authorised partner of ISACA. The CISM exam is administered by ISACA via online remote proctoring or test centres.
KEEP EXPLORING
More ways to move forward.
Related training from the course catalog.
Certified Information Systems Security Professional (CISSP)
Five-day course covering the eight CISSP domains with labs, case studies and daily exam practice to build confidence for certification.
Certified Ethical Hacker (CEH)
Five-day course to practise ethical hacking: reconnaissance, scanning, exploitation, web and wireless attacks, with hands-on labs and exam prep.
CompTIA Security+
A 4-day course building Security+ skills through labs on threats, architecture, operations and governance, with daily exam practice.
CISA Exam Preparation
A 3-day course to review CISA domains, practise audit scenarios, and work through exam-style questions with feedback and a timed mock.