Certification preparation
Elastic Certified SIEM Analyst Exam Preparation
A 3-day, 24-hour course to practise SIEM workflows: ingest data, query with KQL, build detections, visualise, and investigate.
THE BIG PICTURE
About this course
Elastic Certified SIEM Analyst is a professional certification awarded by Elastic for practitioners who use the Elastic Security capabilities to investigate threats, manage detections, and communicate findings. This three-day course builds the skills needed for the exam and day-to-day SOC work. You will explore stack architecture, ECS, data ingestion, KQL in Discover, visualisations and dashboards, detections and alerts, Timeline, Cases, and threat-hunting workflows. Labs run throughout with realistic security datasets and guided practice. The certification exam is purchased and scheduled directly with Elastic. It is administered by Elastic or its exam delivery partner; booking and policies are provided by the awarding body. Candidates should check the current exam guide for format, duration, scoring, and identification requirements. Elastic owns the certification scheme. MindClick provides training and exam preparation and is not an accredited or authorised partner.
What you’ll learn
- Explain how the Elastic Security architecture and components fit within the stack
- Apply ECS to normalise security data and verify mappings
- Ingest common log and endpoint sources using Integrations and confirm data quality
- Build KQL searches in Discover and pivot findings into visualisations and dashboards
- Configure detection rules, schedules, alerts, exceptions, and triage views
- Use Timeline and Cases to investigate, document, and report incidents
- Plan and execute threat-hunting workflows mapped to ATT&CK techniques
- Practise exam-style tasks and create a personal study and booking plan
A CLEAR PATH FORWARD
3-day course agenda
3 instructor-led days (24 contact hours) mapped to the exam domains. Each day combines short concept sessions, hands-on practice on a running case study and exam-style questions.
- Learning route
- 3 recommended days
- Practical work
- 3 guided activities
- Finish with
- Mock exam + certification exam
Take a look at each day. Open a section to see the topics and practical work.
Day 1Foundations and data explorationArchitecture, ECS, ingestion, KQL/Discover
What we’ll cover
- 09:00–10:30 · Orientation and SIEM architecture in the stack
- 10:45–12:15 · Elastic Common Schema (ECS) and field mapping for security data
- 13:15–14:15 · Ingesting logs and endpoint telemetry via Integrations
- 14:15–14:45 · Normalising data and verifying index patterns
- 15:00–16:00 · KQL fundamentals and search techniques in Discover
- 16:00–16:15 · Building saved searches and filters
- 16:15–17:30 · Exam-style practice questions and discussion
Put it into practice
Ingest a sample endpoint and network dataset using an Integration, map key fields to ECS, and validate results in Discover. Create saved searches and filters that support a basic triage workflow.
You’ll take away
Saved searches, KQL snippets, and an ingestion checklist
Day 2Dashboards and detectionsVisualisations/Dashboards, detections, alerts and exceptions
What we’ll cover
- 09:00–10:30 · Recap and Q&A; advanced KQL, aggregations, and pivots
- 10:45–12:15 · Visualisations with Lens/TSVB and building dashboards from saved searches
- 13:15–14:15 · Designing analyst dashboards for investigations and reporting
- 14:15–14:45 · Security dashboards review and alert triage views
- 15:00–16:00 · Detections: rule types, schedules, alerts, and exceptions
- 16:00–16:15 · Testing and tuning rules against sample datasets
- 16:15–17:30 · Exam-style practice questions and debrief
Put it into practice
Create an investigation dashboard and implement two detection rules with appropriate schedules and exceptions. Generate test alerts and iterate on tuning to reduce noise while preserving fidelity.
You’ll take away
Detections rule pack and an analyst dashboard
Day 3Investigations, threat hunting, and exam readinessTimeline, Cases, hunting workflows, mock exam and booking guidance
What we’ll cover
- 09:00–10:30 · Recap and Q&A; investigation workflows with Timeline and Cases
- 10:45–12:15 · Threat hunting approaches and mapping to MITRE ATT&CK
- 13:15–14:15 · Correlating endpoint, network, and cloud signals; useful pivots
- 14:15–14:45 · Response actions, case management, and reporting practices
- 15:00–16:00 · Full lab: from alert to closure using the security application
- 16:00–16:15 · Exam booking process, policies, and readiness checklist
- 16:15–17:30 · Mock exam and targeted review
Put it into practice
Work an end-to-end incident: triage an alert, build a Timeline, collect evidence, and track actions in a Case. Conclude with a brief report and personal improvement notes.
You’ll take away
Investigation timeline, case notes, and a personal study plan
Bring it all together
Certification exam: Elastic Certified SIEM Analyst, awarded by Elastic. Confirm the current exam format with the awarding body when you book. Every attendee also receives a MindClick certificate of completion for 24 contact hours.
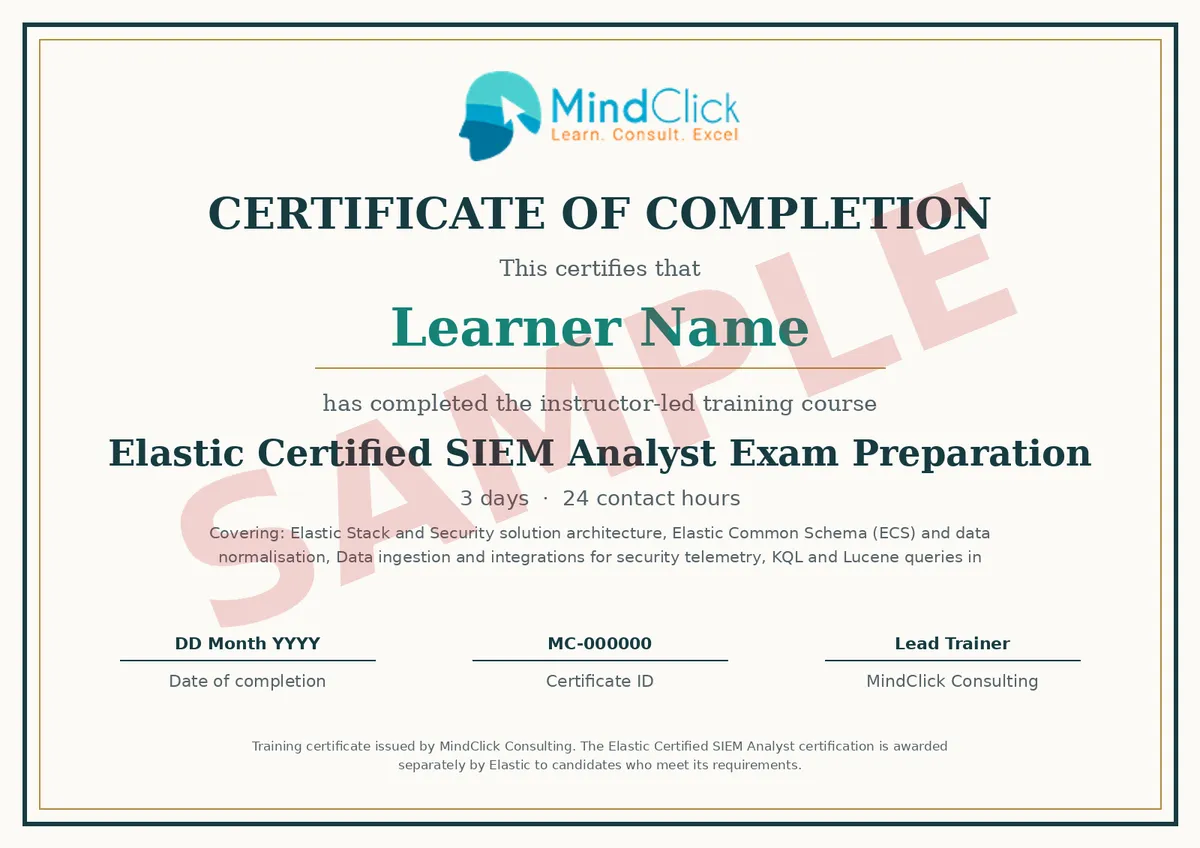
What you receive
You earn two separate credentials. The sample shows the MindClick training certificate.
- MindClick certificate of completion: 3 days, 24 contact hours, issued to every attendee who completes the course.
- Elastic Certified SIEM Analyst: issued by Elastic when you meet its requirements and pass the exam.
Before you choose your learning route
Session timings are indicative; the trainer may adjust them for the group. Exam details reflect the awarding body’s published information at the time of writing; confirm the current version when you book.
Elastic owns this certification scheme. MindClick provides training and exam preparation and is not an accredited or authorised partner of Elastic.
Fees
| Delivery format | Fee per learner | Exam fee |
|---|---|---|
| Live online | $2,800 USD | Included |
| Classroom | $4,500 USD | Included |
One awarding-body certification exam attempt is included in the training fee. Confirm the current fee, any applicable tax and what the fee covers in writing before you pay.
Prerequisites
- While there are no formal prerequisites published by the awarding body, attendees should be comfortable with basic SOC processes and have prior exposure to Kibana or the security application; familiarity with KQL is helpful. Bring a laptop with a modern browser and Wi‑Fi; local admin rights are recommended for lab tooling or access to a cloud-hosted lab.
Who is this course for?
- Security analysts working day to day in Elastic Security.
- SOC practitioners handling detection rules, Timeline, and Cases.
- Teams validating Elastic SIEM analysis skills.
FIND YOUR START
Confirmed batch starts
Choose a published start, then review your offer in the same enrollment flow. A start date is not the full timetable or a seat reservation.
Choose your country & monthStarts
- Training location
- Manama, Bahrain
- Local timezone
- Asia/Bahrain
Joining details and full session timetable to be supplied.
Starts
- Training location
- Cairo, Egypt
- Local timezone
- Africa/Cairo
Joining details and full session timetable to be supplied.
Starts
- Training location
- Kuwait City, Kuwait
- Local timezone
- Asia/Kuwait
Joining details and full session timetable to be supplied.
Starts
- Training location
- Muscat, Oman
- Local timezone
- Asia/Muscat
Joining details and full session timetable to be supplied.
Starts
- Training location
- Doha, Qatar
- Local timezone
- Asia/Qatar
Joining details and full session timetable to be supplied.
Starts
- Training location
- Riyadh, Saudi Arabia
- Local timezone
- Asia/Riyadh
Joining details and full session timetable to be supplied.
Frequently asked questions
How long is the course?
3 days, 24 contact hours, normally 09:00 to 17:30 with breaks. The agenda follows the exam domains and the final day includes a mock exam.
Is the exam included?
Yes. Outside India the fee includes one certification exam attempt. Retakes are booked and paid directly with the awarding body.
What does this course cost?
Outside India this 3-day course is listed at USD 2,800 per learner for live online delivery and USD 4,500 for classroom delivery. Both fees include one certification exam attempt. Pricing for India is confirmed separately by an advisor. Taxes and the final offer are confirmed in writing before you pay.
Are there prerequisites?
While there are no formal prerequisites published by the awarding body, attendees should be comfortable with basic SOC processes and have prior exposure to Kibana or the security application; familiarity with KQL is helpful. Bring a laptop with a modern browser and Wi‑Fi; local admin rights are recommended for lab tooling or access to a cloud-hosted lab.
What certificate will I receive?
Two credentials. MindClick issues a certificate of completion for 24 contact hours to every attendee. Elastic issues the Elastic Certified SIEM Analyst certification when you pass the exam and meet its requirements.
Is MindClick an accredited training partner for this certification?
MindClick provides training and exam preparation and is not an accredited/authorised partner of Elastic; the exam is purchased and administered directly by Elastic.
Where is classroom training delivered?
Singapore and Dubai are the priority classroom markets for this catalog. Classroom delivery is also available in the other listed countries, and live online delivery is available everywhere. Venues are confirmed per booking; a listed city is a training market, not an owned campus.
KEEP EXPLORING
More ways to move forward.
Related training from the course catalog.
Elasticsearch Engineer Training
This 4-day course builds practical skills in designing, indexing, querying, scaling, and operating a distributed search and analytics system.
Data Analysis with Kibana
A 4-day course on analysing data with a visual analytics interface: query, design charts and dashboards, explore time series, maps, ML and alerts.
Elastic Observability Engineer Training
A 4-day course where you ingest logs, metrics and traces, analyse them in dashboards, set alerts, and practise end-to-end incident workflows.
Elastic Security for SIEM
Four-day, 32-hour course to ingest data, query events, build dashboards, triage alerts, and hunt threats in a modern SIEM.