Professional skills
Information Security Systems (ISO 27001) in Switzerland
Showing starts assigned to Switzerland. Change country or city · Global course
A 5-day course to plan an ISO/IEC 27001:2022 ISMS, assess risk, select controls, gather evidence, run internal audits and drive improvement.
THE BIG PICTURE
About this course
ISO/IEC 27001 is the international standard for information security management systems, published by ISO and IEC. Individual certifications aligned to the standard are issued by independent certification bodies, not by ISO itself. Over five days you work through ISMS context and scope, risk assessment and treatment, Annex A control themes, documentation, competence, supplier controls, performance evaluation, internal audits, management review and improvement. You will complete hands‑on tasks such as building a risk register, drafting a Statement of Applicability, preparing audit evidence, and practising audit techniques. Exam routes vary by certification body (for example foundation, implementer or auditor tracks). Candidates book with their chosen body or its partners, and formats, rules and renewal periods differ by provider. This course includes guidance on selecting and scheduling an exam but does not include an exam voucher. The awarding body owns the certification scheme. MindClick provides training and exam preparation and is not an accredited or authorised partner.
What you’ll learn
- Define ISMS context, interested parties and scope aligned to ISO/IEC 27001:2022.
- Establish risk criteria and perform risk assessment; build and maintain a risk register.
- Select, justify and document controls; produce and update a Statement of Applicability.
- Plan and implement ISMS processes, documentation, competence and supplier controls.
- Collect operational evidence, monitor performance, and conduct internal audits.
- Plan and facilitate management review and drive corrective actions and improvement.
- Map organisational practices to certification audit expectations and prepare evidence packs.
- Prepare for a chosen external ISO/IEC 27001 exam with practice questions and a study plan.
A CLEAR PATH FORWARD
5-day course agenda
5 instructor-led days (40 contact hours) mapped to the exam domains. Each day combines short concept sessions, hands-on practice on a running case study and exam-style questions.
- Learning route
- 5 recommended days
- Practical work
- 5 guided activities
- Finish with
- Mock exam + certification exam
Take a look at each day. Open a section to see the topics and practical work.
Day 1ISMS foundations and scopeContext and scope; leadership and policy
What we’ll cover
- 09:00–09:30 · Course orientation, learning goals and ISO/IEC 27001:2022 at a glance
- 09:30–10:45 · ISMS principles, Clauses 4–10 structure and Annex A themes
- 11:00–12:30 · Organisational context and interested parties (Clause 4.1–4.2)
- 13:30–14:15 · Defining ISMS scope and boundaries (Clause 4.3) with case examples
- 14:15–15:15 · Information assets, processes and interfaces mapped to scope
- 15:30–16:30 · Leadership, roles, responsibilities and policy (Clause 5)
- 16:30–17:30 · Exam-style practice questions and group debrief
Put it into practice
Facilitated scoping workshop: identify interested parties, needs and expectations, then draft an ISMS scope statement. Peer review to refine boundaries and interfaces.
You’ll take away
Draft context, interested parties and scope pack
Day 2Risk assessment and treatmentPlanning, risk, objectives and control selection
What we’ll cover
- 09:00–09:20 · Recap and Q&A from Day 1
- 09:20–10:45 · Planning, risk criteria and information security objectives (Clause 6)
- 11:00–12:30 · Risk assessment methods: identification, analysis and evaluation
- 13:30–14:15 · Building the risk register: assets, threats, vulnerabilities and impacts
- 14:15–15:15 · Risk treatment options and control selection (Annex A mapping)
- 15:30–16:30 · Statement of Applicability: content, justification and maintenance
- 16:30–17:30 · Exam-style practice questions and debrief
Put it into practice
Complete a risk assessment for a sample process and record results in a risk register. Draft the first version of the Statement of Applicability with justifications.
You’ll take away
Risk register and initial Statement of Applicability
Day 3Support, documentation and operationClause 7–8 processes and Annex A control implementation
What we’ll cover
- 09:00–09:20 · Recap and Q&A from Day 2
- 09:20–10:45 · Support: resources, competence, awareness and communication (Clause 7)
- 11:00–12:30 · Documented information: policies, procedures, records and control
- 13:30–14:15 · Operational planning and control (Clause 8); change and outsourced processes
- 14:15–15:15 · Annex A controls: organisational, people, physical and technological
- 15:30–16:30 · Supplier risk, cloud services and information security in contracts
- 16:30–17:30 · Exam-style practice questions and debrief
Put it into practice
Draft two ISMS procedures (document control and supplier management) and a control implementation plan for a chosen area. Validate coverage against risks and SoA.
You’ll take away
ISMS procedure set and control implementation plan
Day 4Performance, audit and improvementMonitoring, internal audit, management review and improvement
What we’ll cover
- 09:00–09:20 · Recap and Q&A from Day 3
- 09:20–10:45 · Monitoring, measurement, analysis and evaluation (Clause 9.1)
- 11:00–12:30 · Internal audit programme, criteria, evidence and sampling (Clause 9.2)
- 13:30–14:15 · Management review inputs, outputs and records (Clause 9.3)
- 14:15–15:15 · Nonconformity, corrective action and continual improvement (Clause 10)
- 15:30–16:10 · Audit interviewing, note-taking and traceability practice
- 16:10–17:30 · Exam-style practice questions, scenario discussion and debrief
Put it into practice
Run a short internal audit role‑play against selected clauses and controls, capturing objective evidence. Produce a brief audit report with findings and actions.
You’ll take away
Internal audit checklist and sample audit findings log
Day 5Certification pathway and readinessReadiness evidence, certification audits, exam and next steps
What we’ll cover
- 09:00–09:20 · Recap and Q&A from Day 4
- 09:20–10:45 · ISMS effectiveness metrics, dashboards and evidence packs
- 11:00–12:00 · Certification audit process: Stage 1, Stage 2, surveillance and recertification
- 12:00–12:30 · Integrating with other standards via Annex SL high-level structure
- 13:30–14:15 · Common nonconformities and practical preventive controls
- 14:15–15:15 · Exam options overview and choosing a certification route
- 15:30–16:30 · Mock exam (timed) and review of correct answers
- 16:30–17:30 · Individual exam booking guidance and personal study plan
Put it into practice
Complete a Stage 1 readiness self‑assessment using your draft evidence pack. Create a tailored certification roadmap and register with a chosen exam provider.
You’ll take away
Personal ISMS improvement and exam preparation plan
Bring it all together
Certification exam: Information Security Systems (ISO 27001). Confirm the current exam format with the awarding body when you book. Every attendee also receives a MindClick certificate of completion for 40 contact hours.
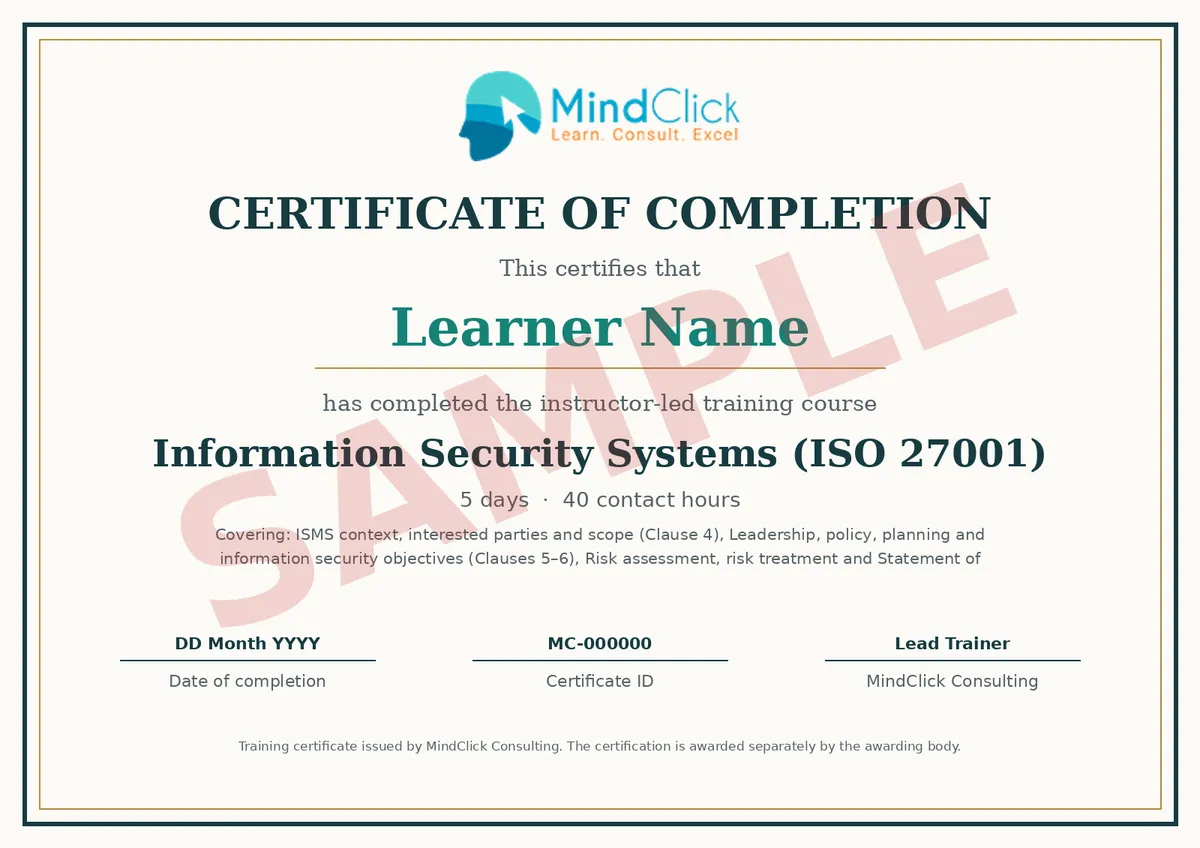
What you receive
You earn two separate credentials. The sample shows the MindClick training certificate.
- MindClick certificate of completion: 5 days, 40 contact hours, issued to every attendee who completes the course.
- Information Security Systems (ISO 27001): issued by the awarding body when you meet its requirements and pass the exam.
Before you choose your learning route
Certification route: There is no single ISO/IEC 27001 individual exam; routes vary by certification body, and many require attendance on an approved course.
Session timings are indicative; the trainer may adjust them for the group. Exam details reflect the awarding body’s published information at the time of writing; confirm the current version when you book.
The awarding body owns this certification scheme. MindClick provides training and exam preparation and is not an accredited or authorised partner of the awarding body.
Fees
| Delivery format | Fee per learner | Exam fee |
|---|---|---|
| Live online | $2,800 USD ≈ €2,485 |
Included |
| Classroom | $4,500 USD ≈ €3,995 |
Included |
Local amounts are indicative only, converted at the rate captured on 2026-10-02. You are charged in USD and your bank sets the final rate.
One awarding-body certification exam attempt is included in the training fee. Confirm the current fee, any applicable tax and what the fee covers in writing before you pay.
Prerequisites
- No formal prerequisites for this course. Recommended: familiarity with information security concepts and management systems, plus experience in IT, security, compliance or quality; exam prerequisites vary by certification body. Please bring a laptop with a spreadsheet tool and a PDF reader.
FIND YOUR START
Confirmed batch starts
Choose a published start, then review your offer in the same enrollment flow. A start date is not the full timetable or a seat reservation.
Choose your country & monthStarts
- Training location
- Zurich, Switzerland
- Local timezone
- Europe/Zurich
Venue and full session timetable to be supplied.
Starts
- Training location
- Zurich, Switzerland
- Local timezone
- Europe/Zurich
Joining details and full session timetable to be supplied.
Starts
- Training location
- Zurich, Switzerland
- Local timezone
- Europe/Zurich
Joining details and full session timetable to be supplied.
Starts
- Training location
- Zurich, Switzerland
- Local timezone
- Europe/Zurich
Venue and full session timetable to be supplied.
Starts
- Training location
- Zurich, Switzerland
- Local timezone
- Europe/Zurich
Venue and full session timetable to be supplied.
Starts
- Training location
- Zurich, Switzerland
- Local timezone
- Europe/Zurich
Joining details and full session timetable to be supplied.
Frequently asked questions
How long is the course?
5 days, 40 contact hours, normally 09:00 to 17:30 with breaks. The agenda follows the exam domains and the final day includes a mock exam.
Is the exam included?
Yes. Outside India the fee includes one certification exam attempt. Retakes are booked and paid directly with the awarding body. There is no single ISO/IEC 27001 individual exam; routes vary by certification body, and many require attendance on an approved course.
Are there prerequisites?
No formal prerequisites for this course. Recommended: familiarity with information security concepts and management systems, plus experience in IT, security, compliance or quality; exam prerequisites vary by certification body. Please bring a laptop with a spreadsheet tool and a PDF reader.
What certificate will I receive?
Two credentials. MindClick issues a certificate of completion for 40 contact hours to every attendee. The awarding body issues the Information Security Systems (ISO 27001) certification when you pass the exam and meet its requirements.
Is MindClick an accredited training partner for this certification?
MindClick provides training and exam preparation and is not an accredited/authorised partner of any awarding body; ISO/IEC 27001-aligned exams are administered by independent certification bodies (for example PECB, EXIN, BSI or IBITGQ).
KEEP EXPLORING
More ways to move forward.
Related training from the course catalog.

Certified Information Systems Security Professional (CISSP)
Five-day course covering the eight CISSP domains with labs, case studies and daily exam practice to build confidence for certification.
Certified Ethical Hacker (CEH)
Five-day course to practise ethical hacking: reconnaissance, scanning, exploitation, web and wireless attacks, with hands-on labs and exam prep.
CompTIA Security+
A 4-day course building Security+ skills through labs on threats, architecture, operations and governance, with daily exam practice.
Certified Information Security Manager (CISM)
Five-day course where learners practise information security governance, risk, programme delivery and incident response, with labs and exam prep.